BioGrid’s data security – keeping patient data secure
April 28, 2025
Data Security is of critical importance to the services BioGrid offers. With millions of patient records being managed through the BioGrid platform, data security is always top of mind for Wisam Abdelaziz, BioGrid’s Head, Infrastructure & Data Engineering.
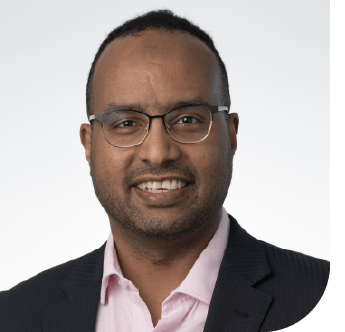
“The health sector is very security conscious now,” says Wisam. “There are obviously serious impacts for individuals if health data is leaked.”
A core service of the BioGrid data sharing platform is linking data sets in a privacy-protected manner across institutions and jurisdictions to facilitate multi-site research.
All data is de-identified in the BioGrid platform and allocated a unique record matching key, enabling an individual’s record to be linked across multiple databases or sites without revealing any identifying information.
Proactive data protection
BioGrid’s information security policy specifies the company’s security environment, and the cyber incident management plan outlines the company’s mitigation plan if there is a data breach.
To minimise the likelihood of a security issue, the BioGrid executive team, supported by the BioGrid Board of Directors, has developed a culture of prevention, with KPIs for all staff reflecting the company’s data security objectives outlined in the BioGrid business plan.
When a new system is implemented, BioGrid engages the services of an objective third party organisation to carry out an independent security review.
“Recently we implemented Microsoft Azure and engaged Cyber CX, one of the largest security services companies in Australia, to review the environment,” says Wisam. “It was a useful exercise because while there were no issues they were able to suggest some really helpful refinements.”
Wisam firmly believes good data security is the result of a multi-dimensional approach.
Once you have all the protections in place, the most important thing to do is constantly monitor what is going on in your business environment – whether it’s technical, or the human element
Wisam Abdelaziz
“You have to keep up-to-date with what threats are emerging and what other businesses are experiencing – it’s important to learn from what other people have missed. Reinforcing good habits and a security mindset in your team is critical too.”
Read more about how BioGrid ensures data security for our members and collaborators